

More about the book
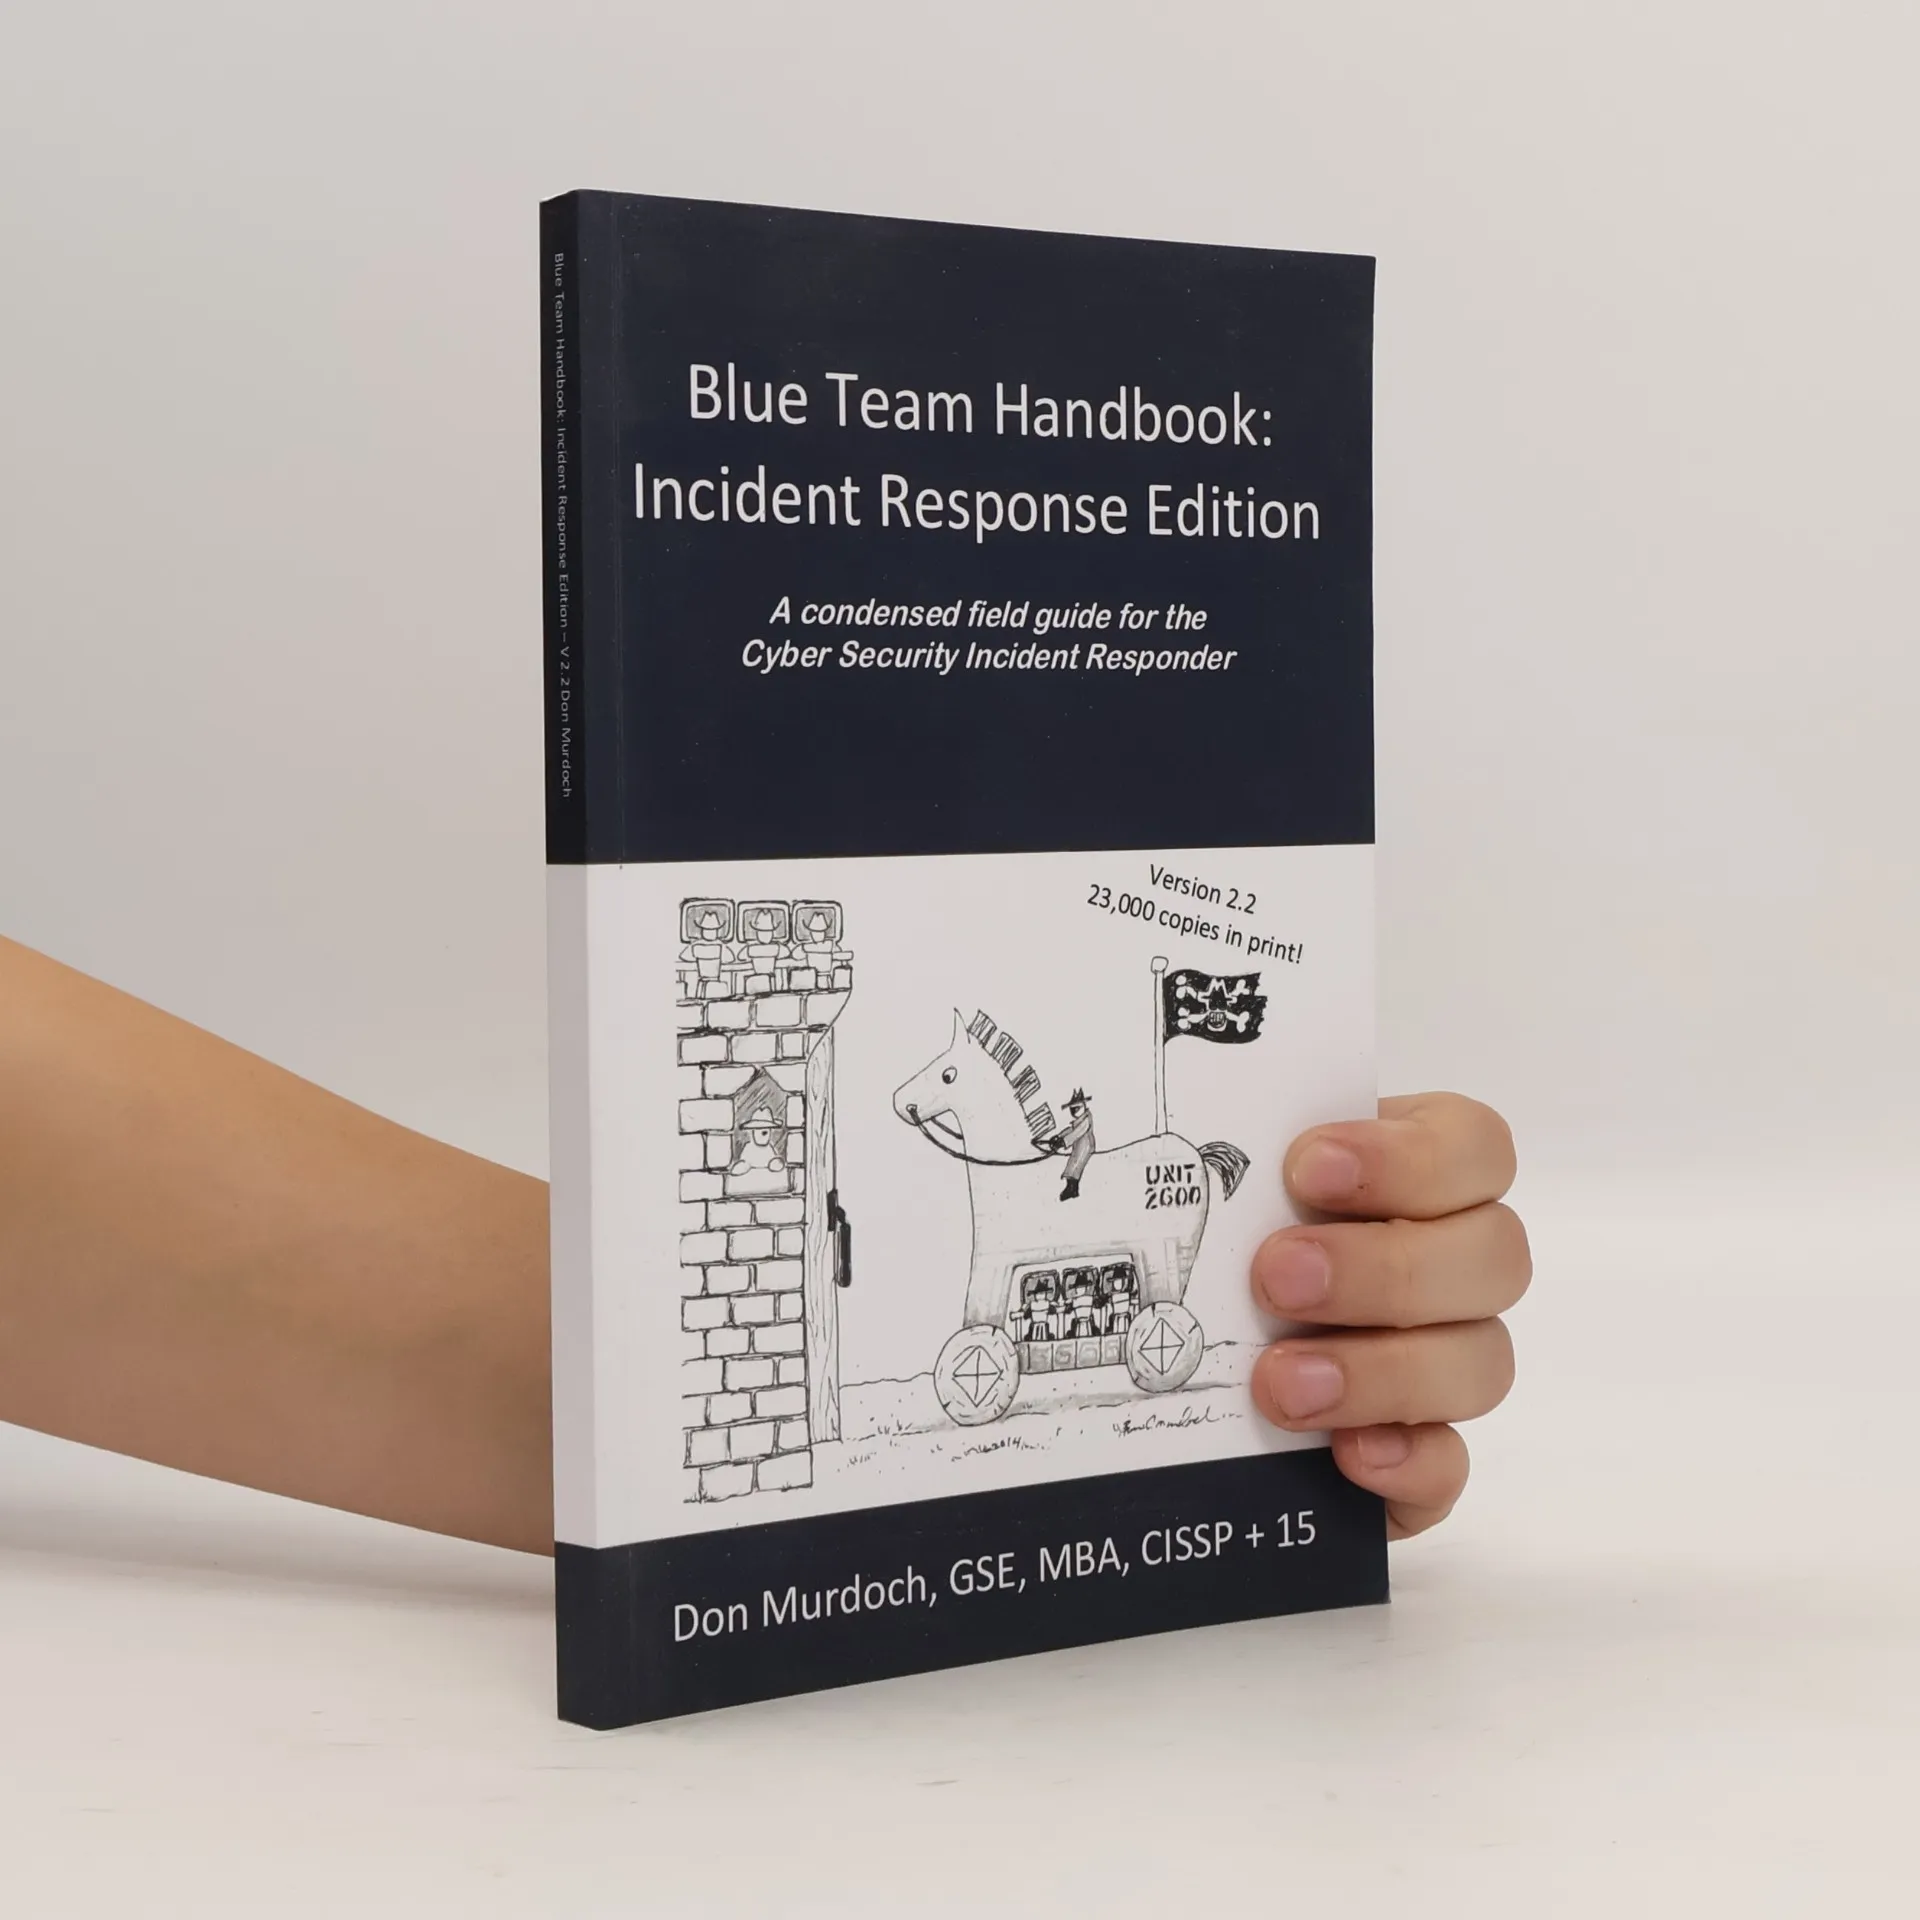
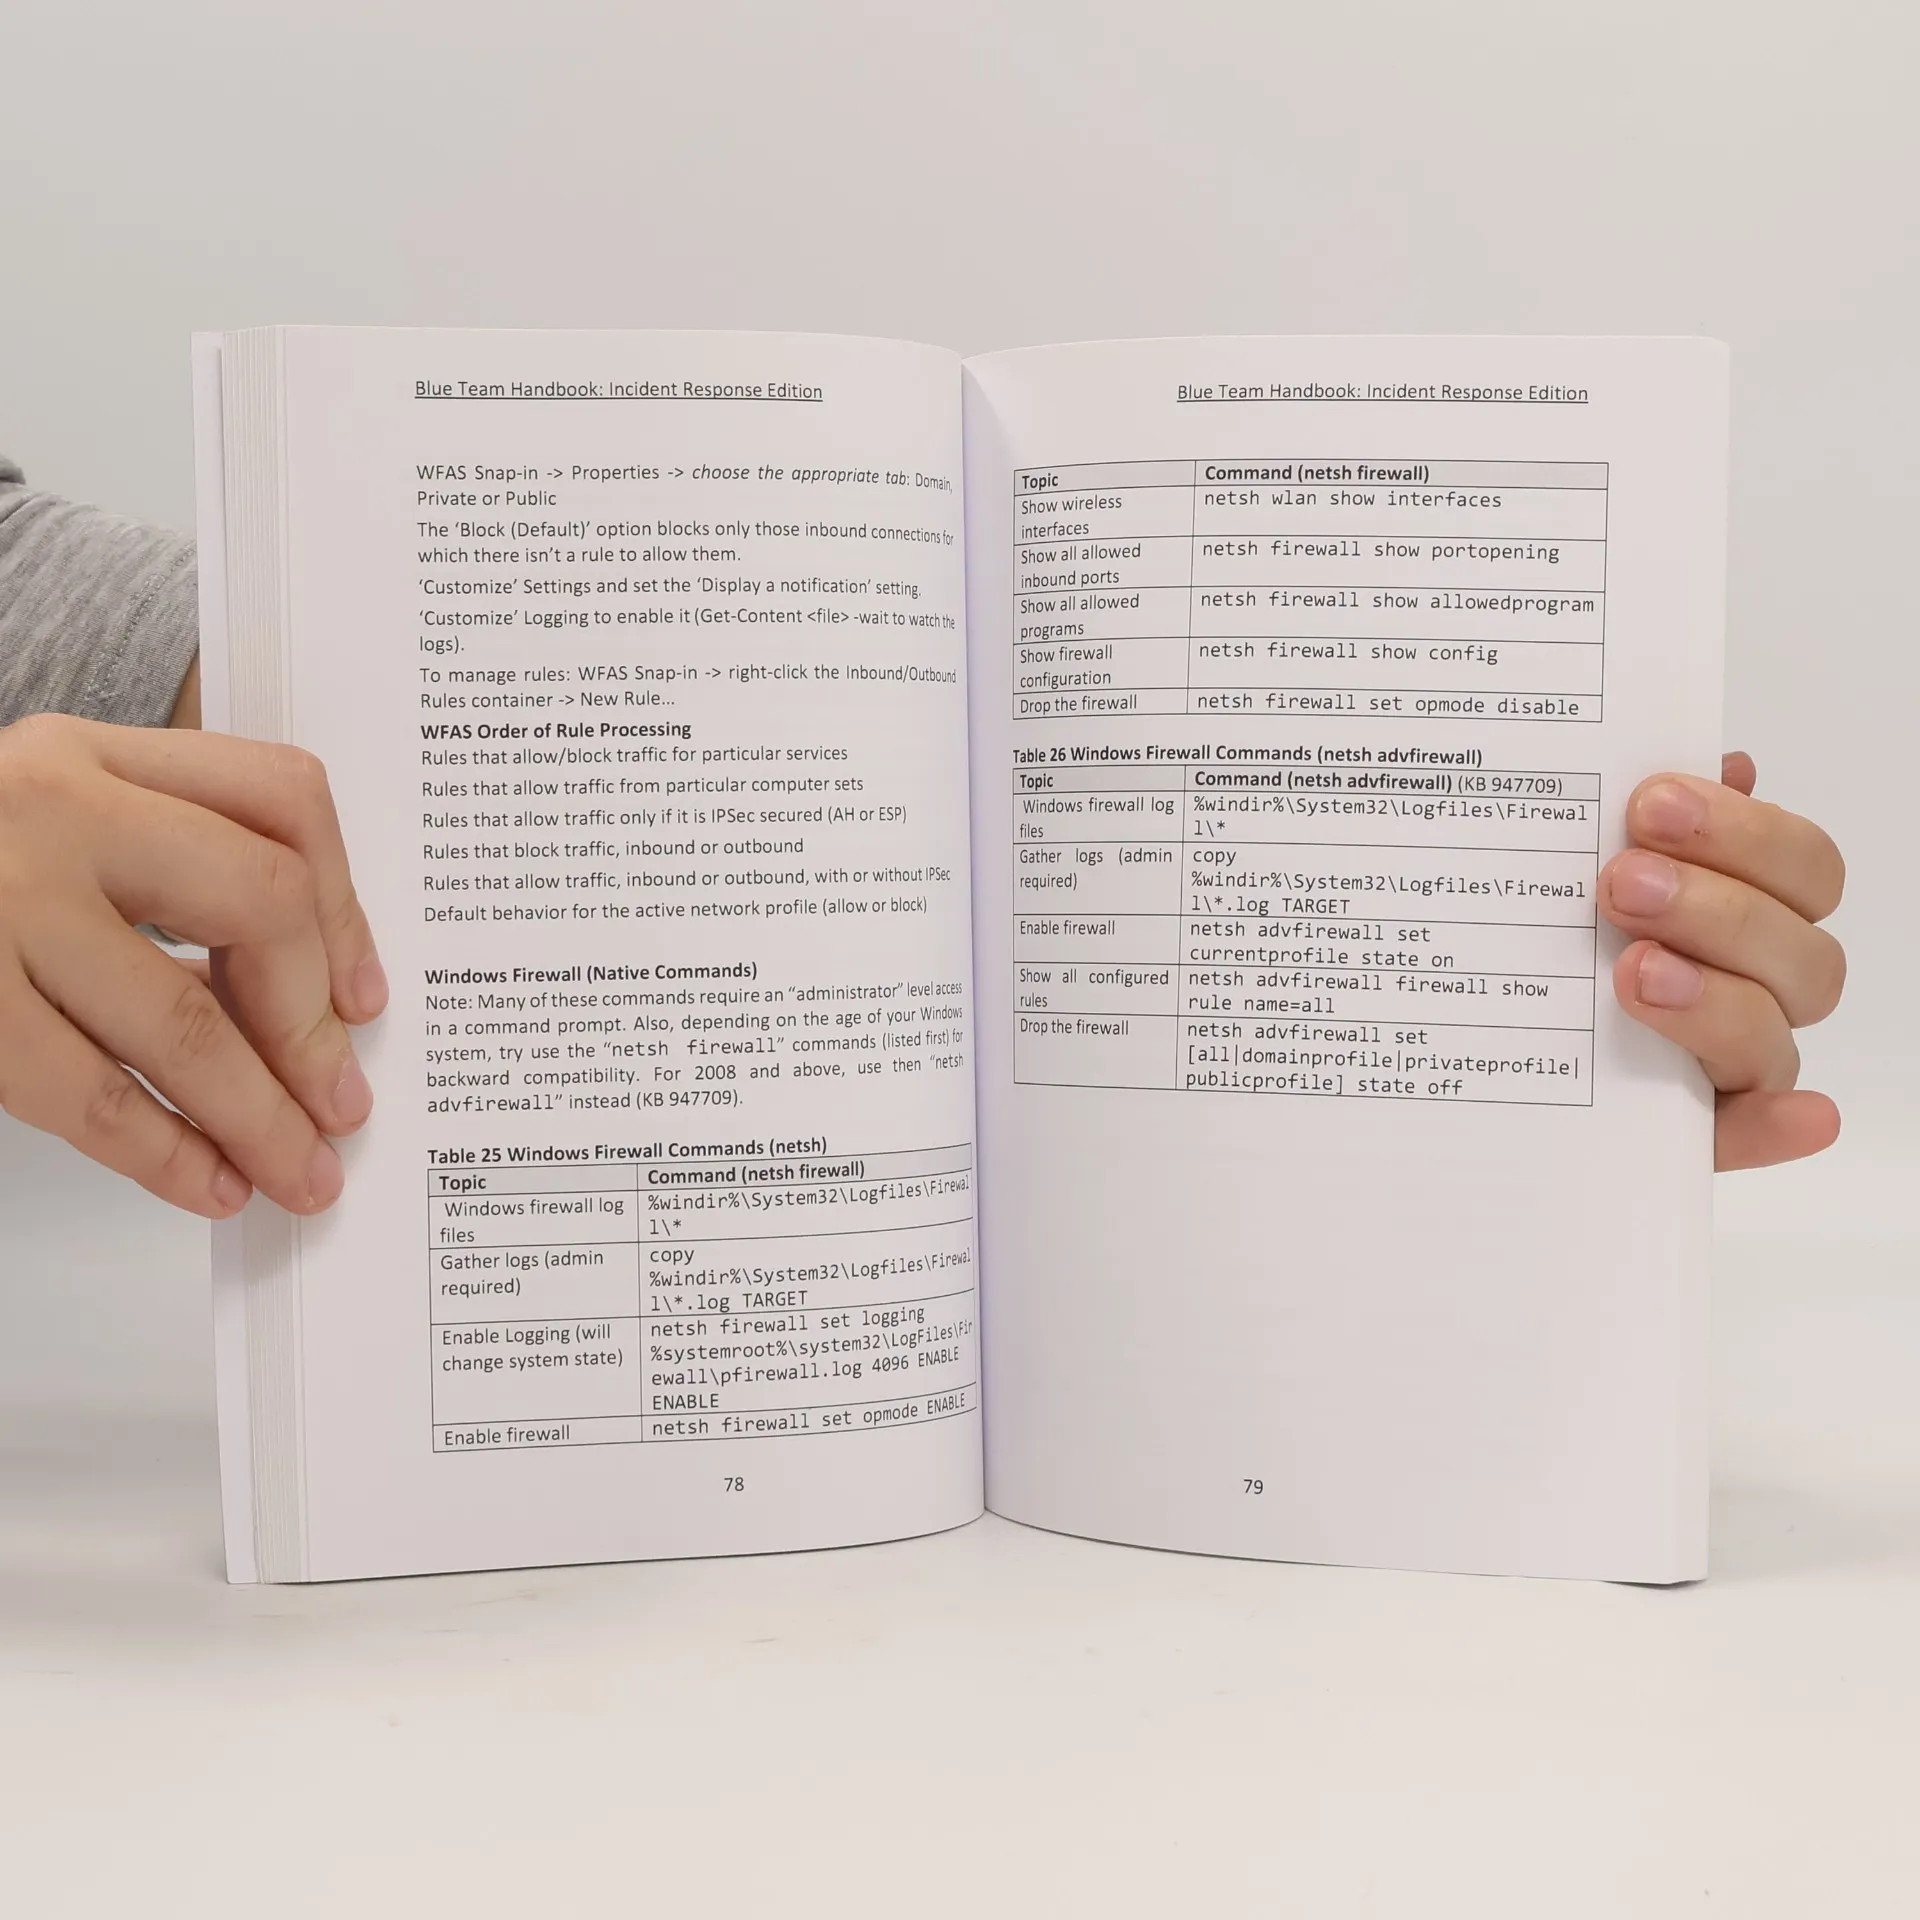
The Blue Team Handbook is a "zero fluff" reference guide for cyber security incident responders, security engineers, and InfoSec pros alike. The BTHb includes essential information in a condensed handbook format. Main topics include the incident response process, how attackers work, common tools for incident response, a methodology for network analysis, common indicators of compromise, Windows and Linux analysis processes, tcpdump usage examples, Snort IDS usage, packet headers, and numerous other quick reference topics. The book is designed specifically to share "real life experience," so it is peppered with practical techniques from the authors' extensive career in handling incidents. Whether you are writing up your cases notes, analyzing potentially suspicious traffic, or called in to look over a misbehaving server - this book should help you handle the case and teach you some new techniques along the way.
Book purchase
Blue Team Handbook, Don W. Murdoch
- Language

- Released
- 2014
- Binding
- (Paperback),
- Book condition
- Very Good
- Price
- €7.69
Payment methods
No one has rated yet.
- Title
- Blue Team Handbook
- Subtitle
- Incident Response Edition: A Condensed Field Guide for the Cyber Security Incident Responder
- Language
- English
- Authors
- Don W. Murdoch
- Released
- 2014
- Format
- Paperback
- Pages
- 164
- ISBN10
- 1500734756
- ISBN13
- 9781500734756
- Series
- Description
- The Blue Team Handbook is a "zero fluff" reference guide for cyber security incident responders, security engineers, and InfoSec pros alike. The BTHb includes essential information in a condensed handbook format. Main topics include the incident response process, how attackers work, common tools for incident response, a methodology for network analysis, common indicators of compromise, Windows and Linux analysis processes, tcpdump usage examples, Snort IDS usage, packet headers, and numerous other quick reference topics. The book is designed specifically to share "real life experience," so it is peppered with practical techniques from the authors' extensive career in handling incidents. Whether you are writing up your cases notes, analyzing potentially suspicious traffic, or called in to look over a misbehaving server - this book should help you handle the case and teach you some new techniques along the way.