
You'll get the exact copy in the photo
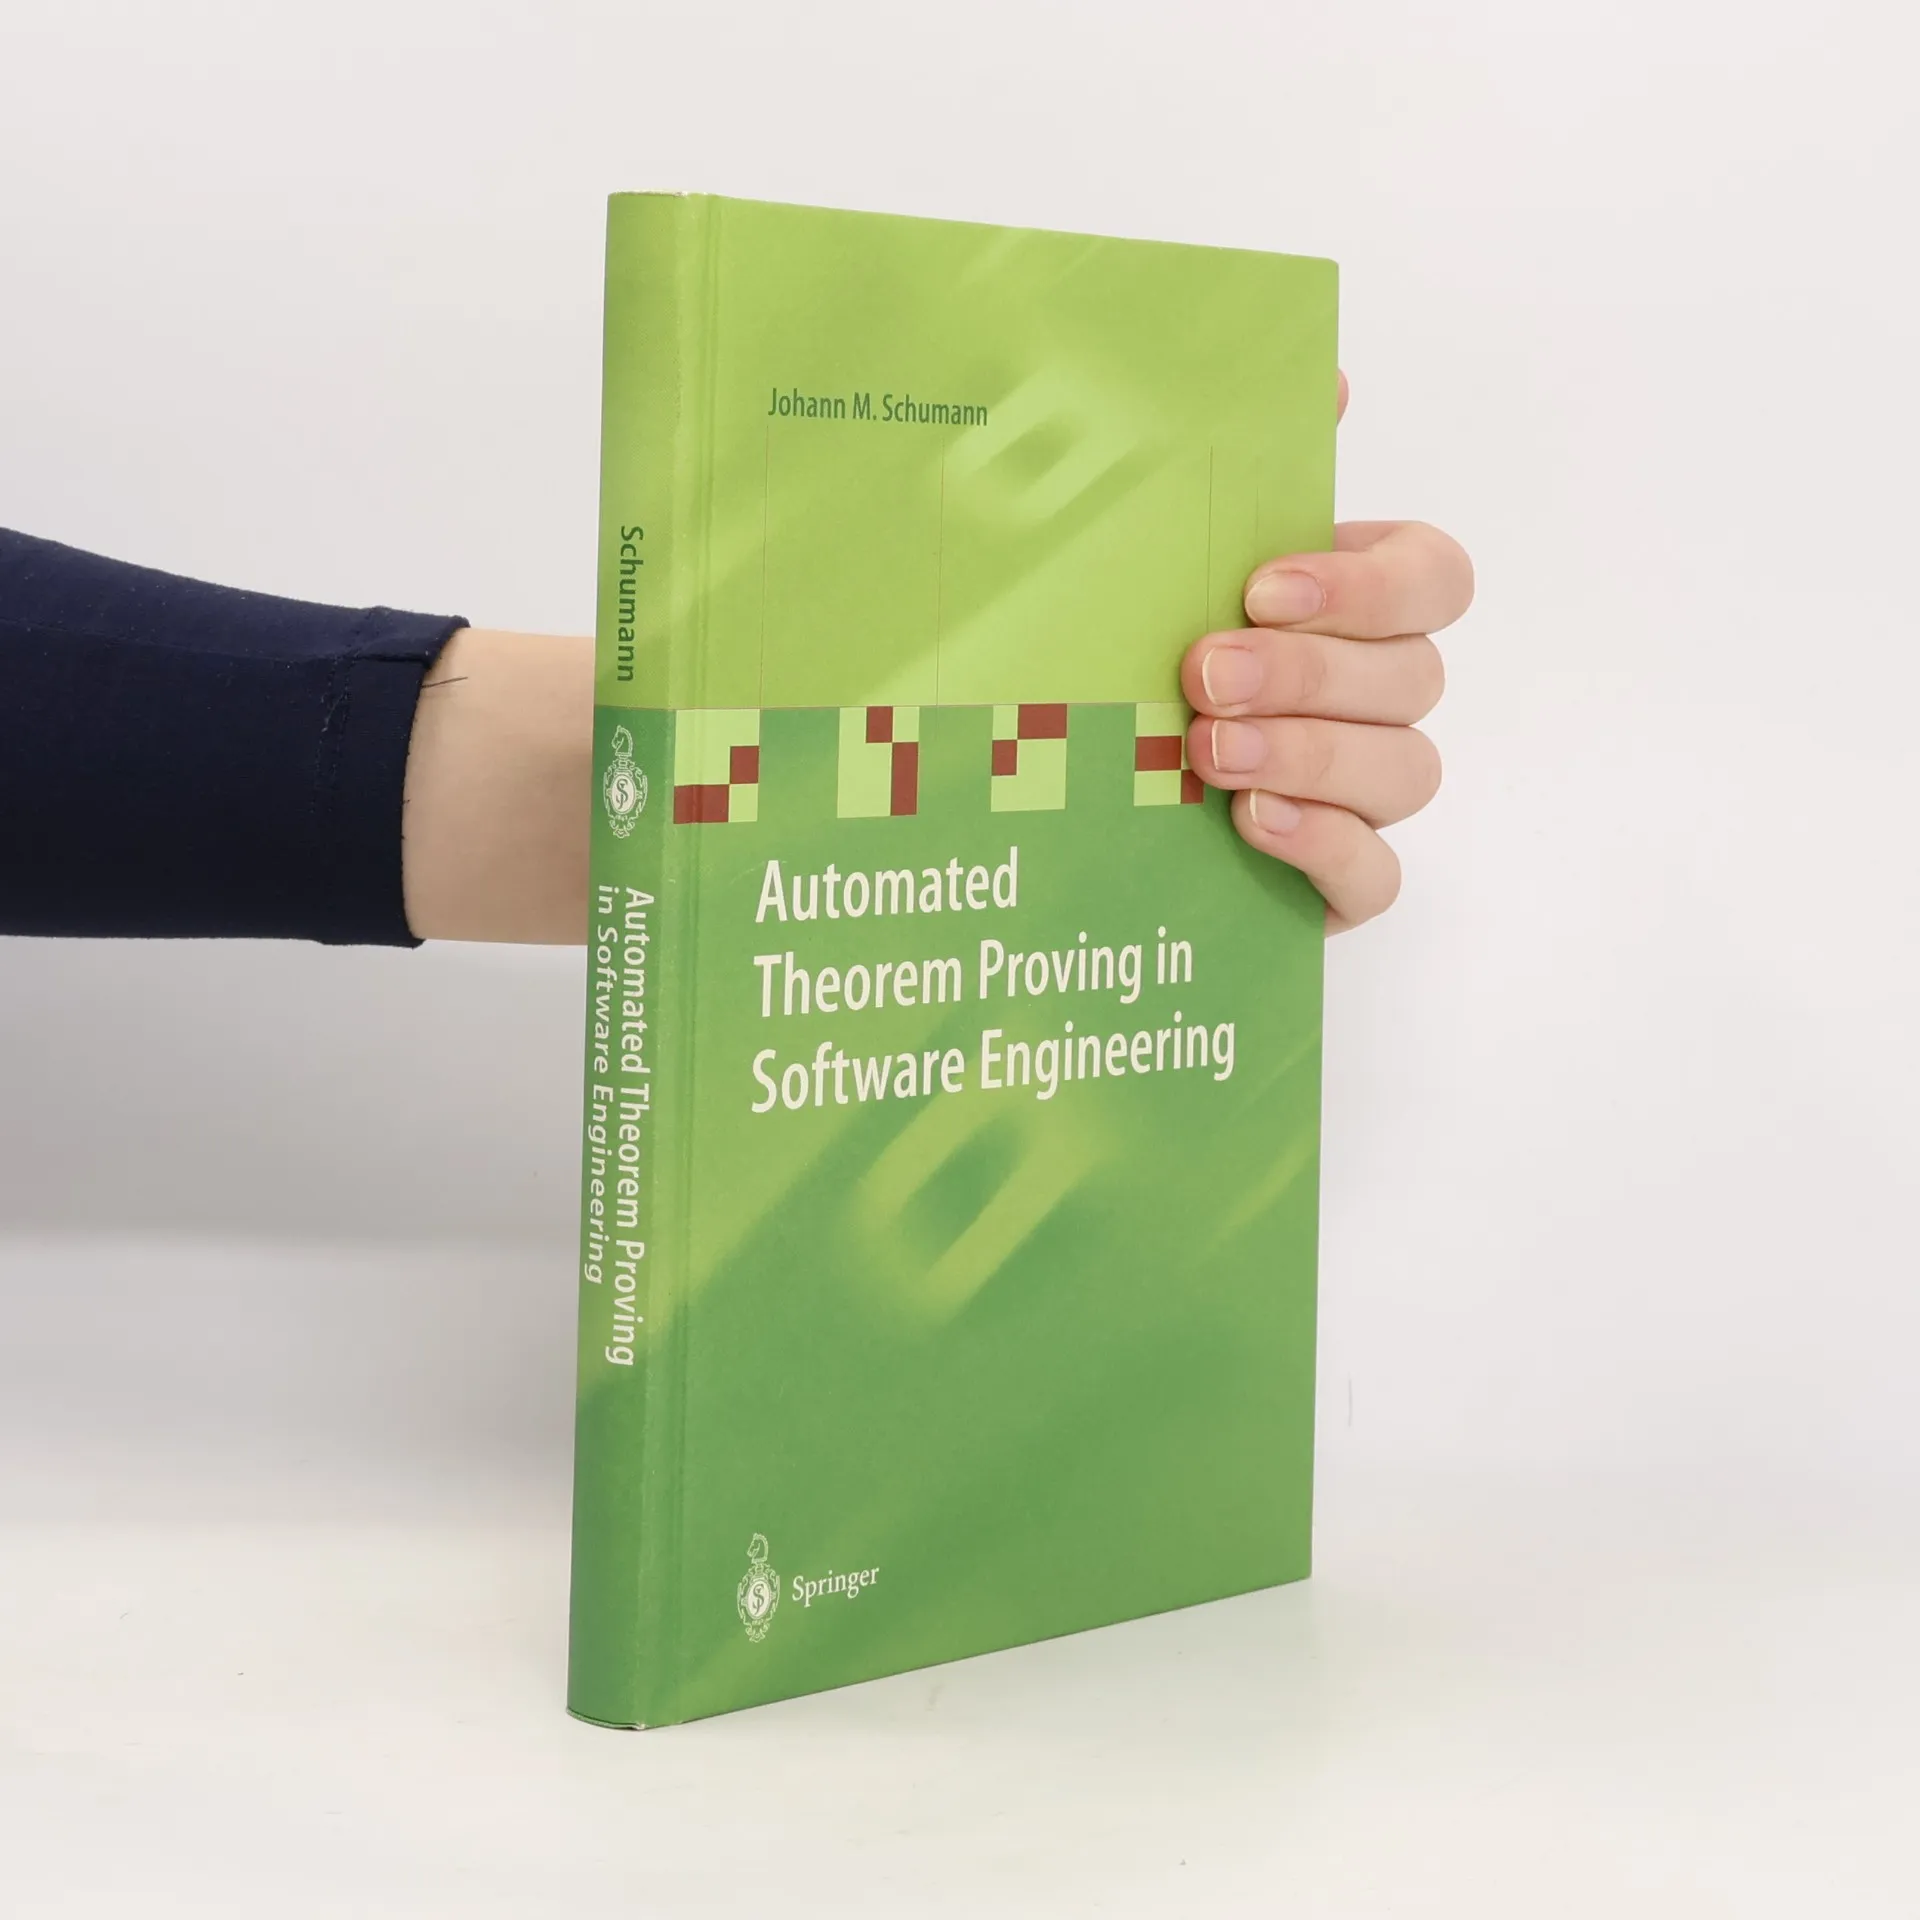
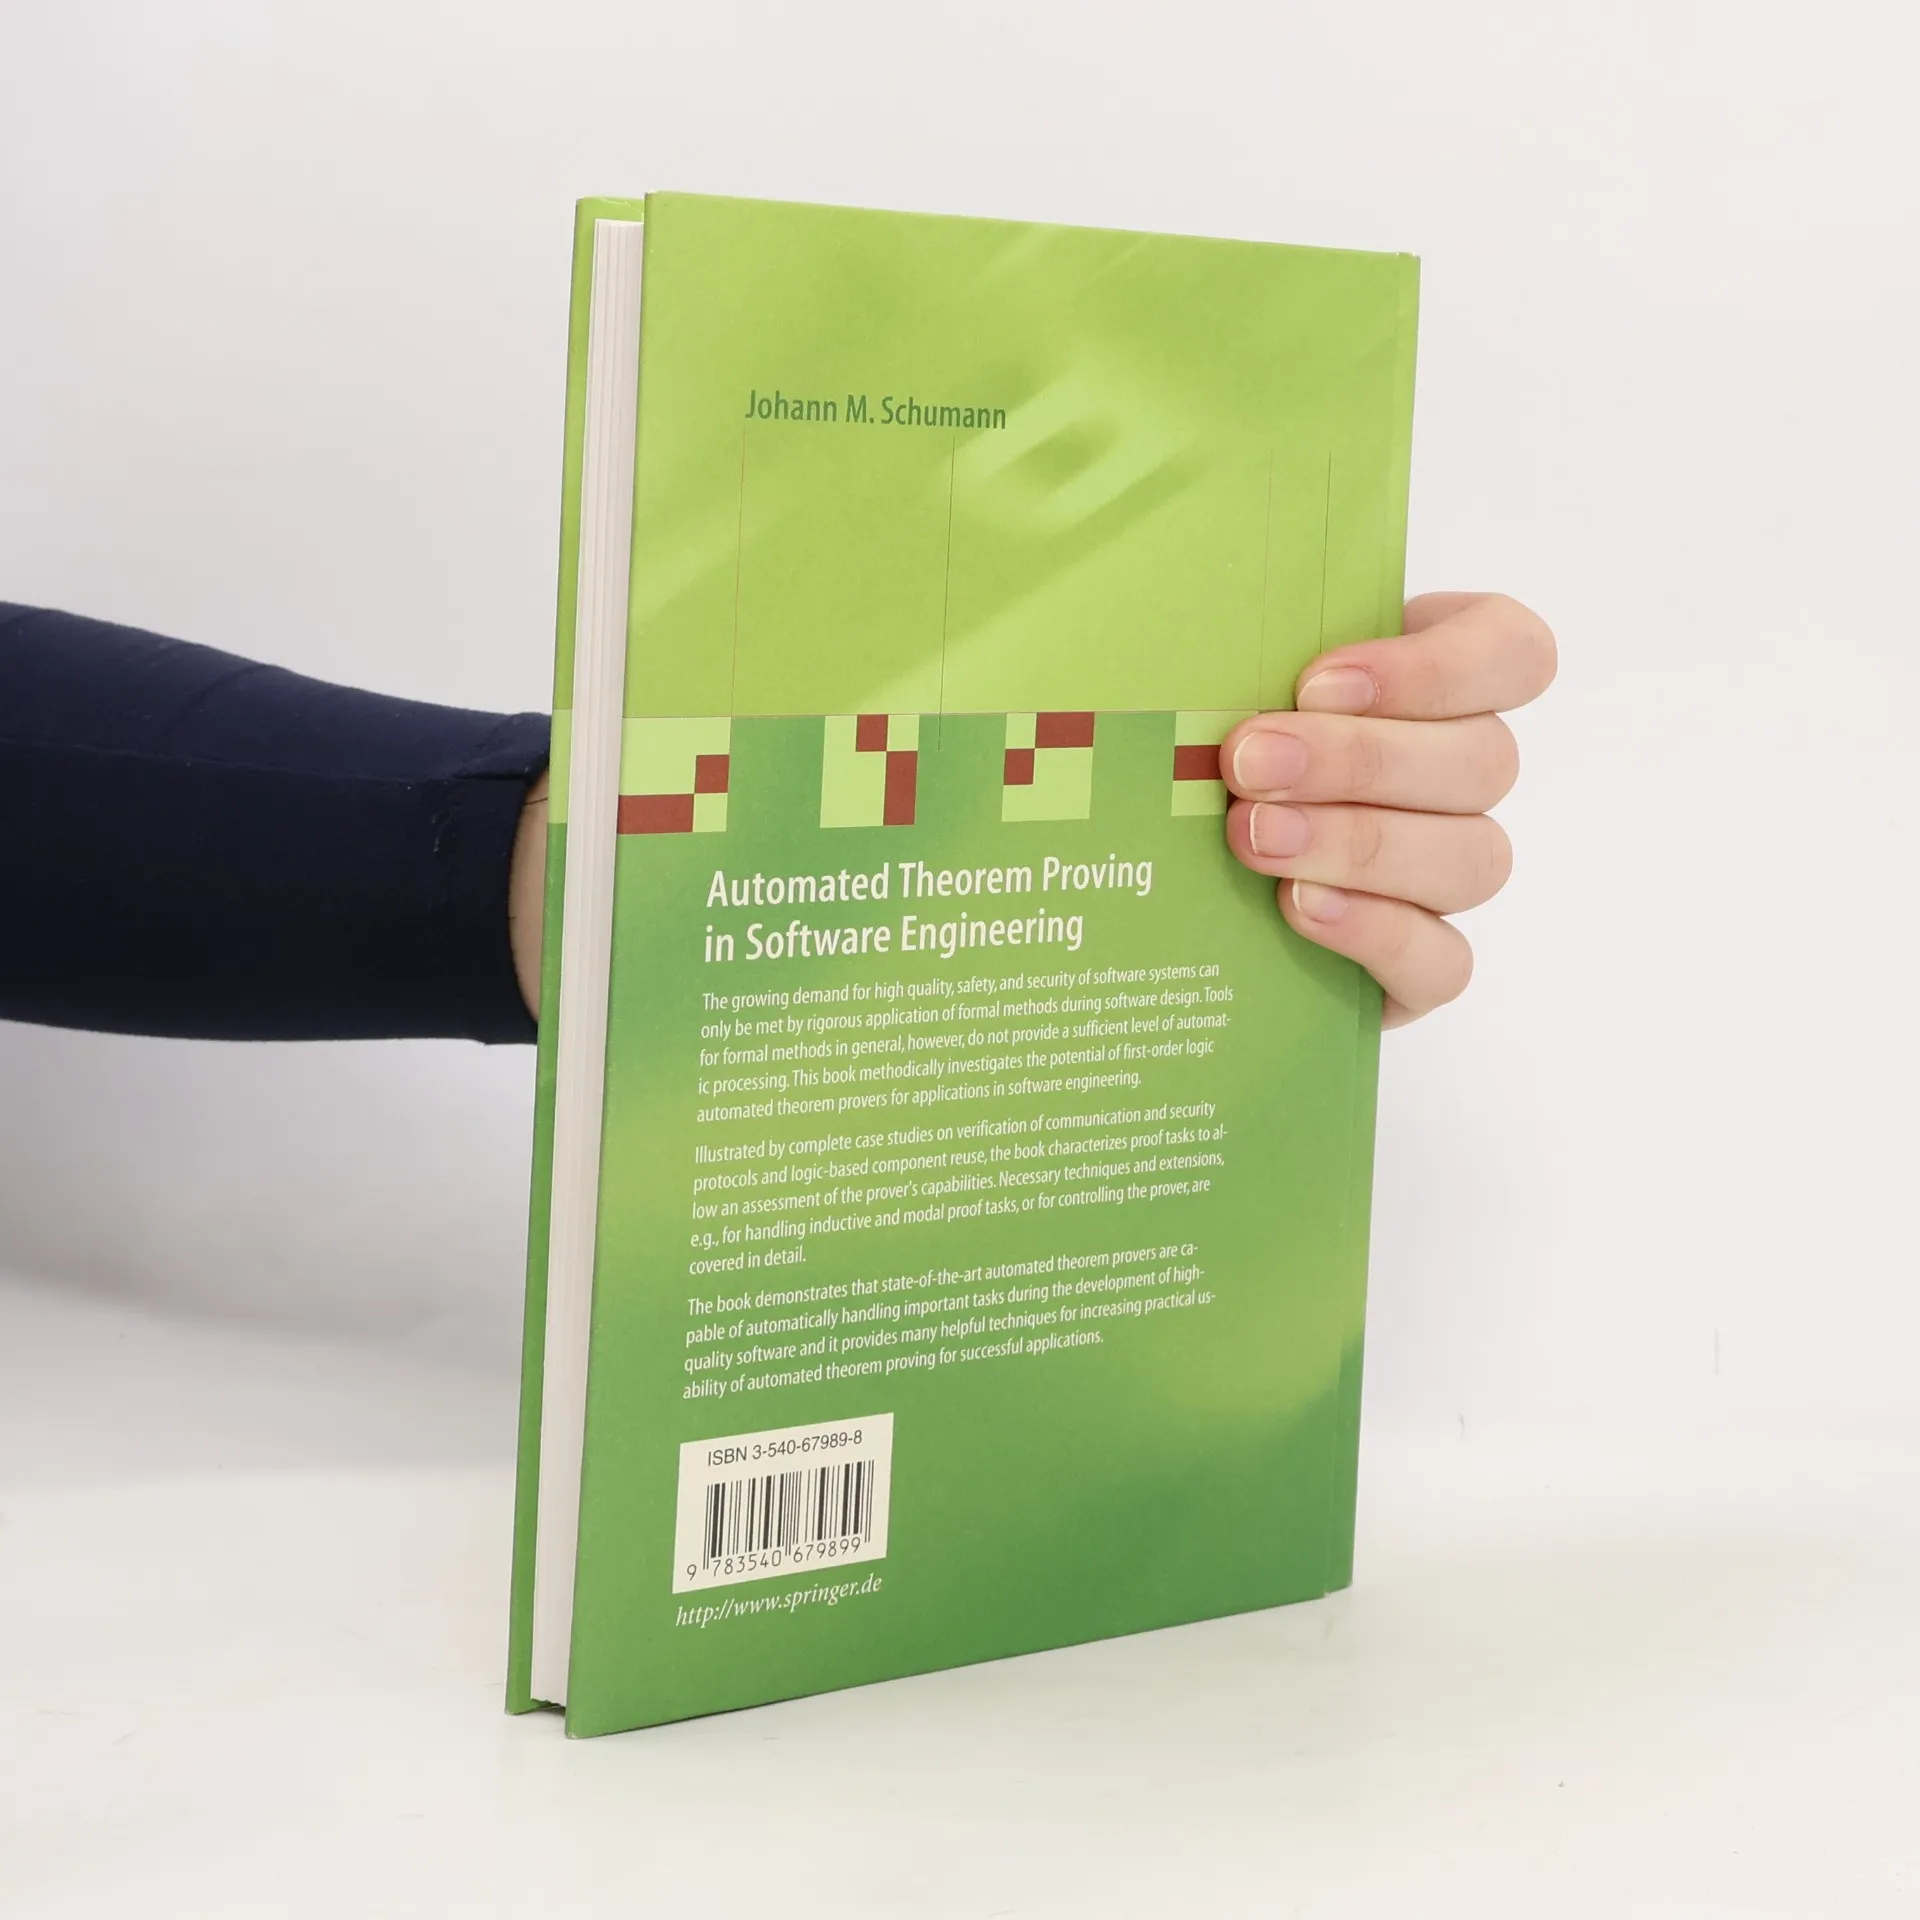
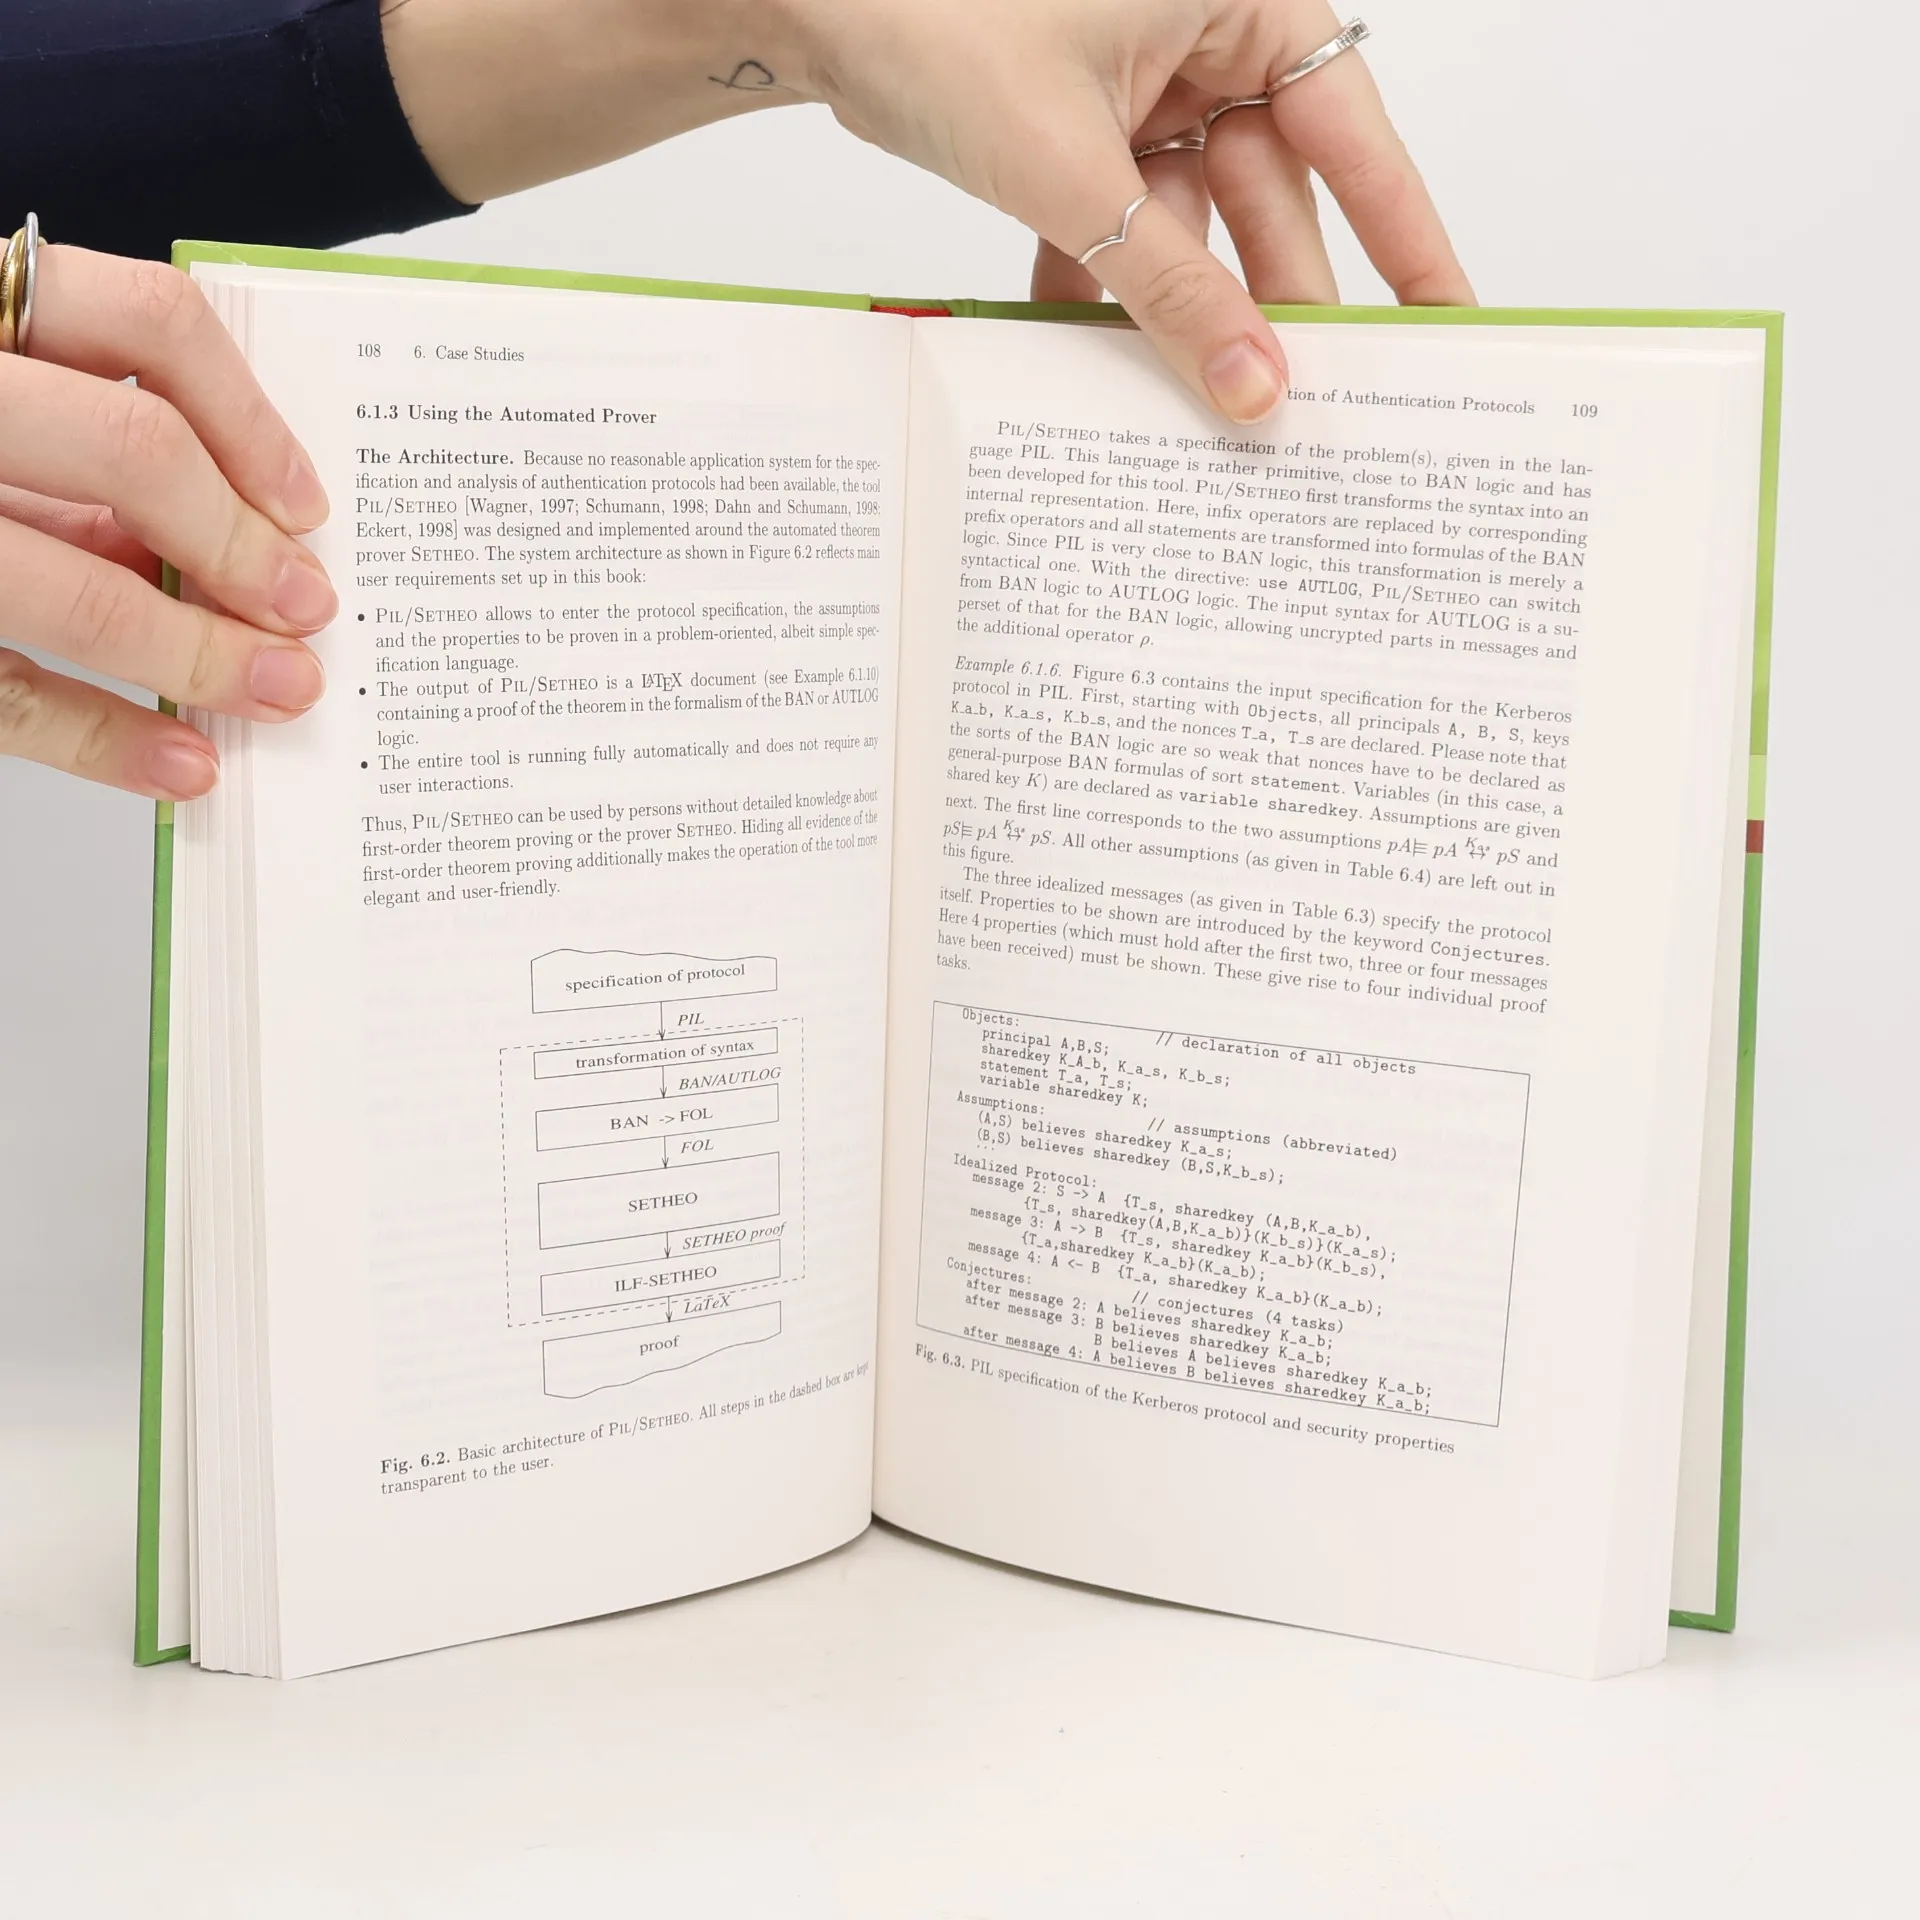
Automated Theorem Proving in Software Engineering
Parameters
- 228 pages
- 8 hours of reading
More about the book
Growing demands for the quality, safety, and security of software can only be satisfied by the rigorous application of formal methods during software design. This book methodically investigates the potential of first-order logic automated theorem provers for applications in software engineering. Illustrated by complete case studies on protocol verification, verification of security protocols, and logic-based software reuse, this book provides techniques for assessing the prover's capabilities and for selecting and developing an appropriate interface architecture.
Book purchase
Automated Theorem Proving in Software Engineering, D. Loveland, Johann M. Ph. Schumann
- Language

- Released
- 2001
- Binding
- (Hardcover),
- Book condition
- Good
- Price
- €31.99
Payment methods
No one has rated yet.
- Title
- Automated Theorem Proving in Software Engineering
- Language
- English
- Authors
- D. Loveland, Johann M. Ph. Schumann
- Publisher
- Springer
- Released
- 2001
- Format
- Hardcover
- Pages
- 228
- ISBN10
- 3540679898
- ISBN13
- 9783540679899
- Series
- Categories
- Tags
- Architecture, Western Europe, Artificial Intelligence, Logic, Operating Systems, Software Development, Information Systems
- Description
- Growing demands for the quality, safety, and security of software can only be satisfied by the rigorous application of formal methods during software design. This book methodically investigates the potential of first-order logic automated theorem provers for applications in software engineering. Illustrated by complete case studies on protocol verification, verification of security protocols, and logic-based software reuse, this book provides techniques for assessing the prover's capabilities and for selecting and developing an appropriate interface architecture.