

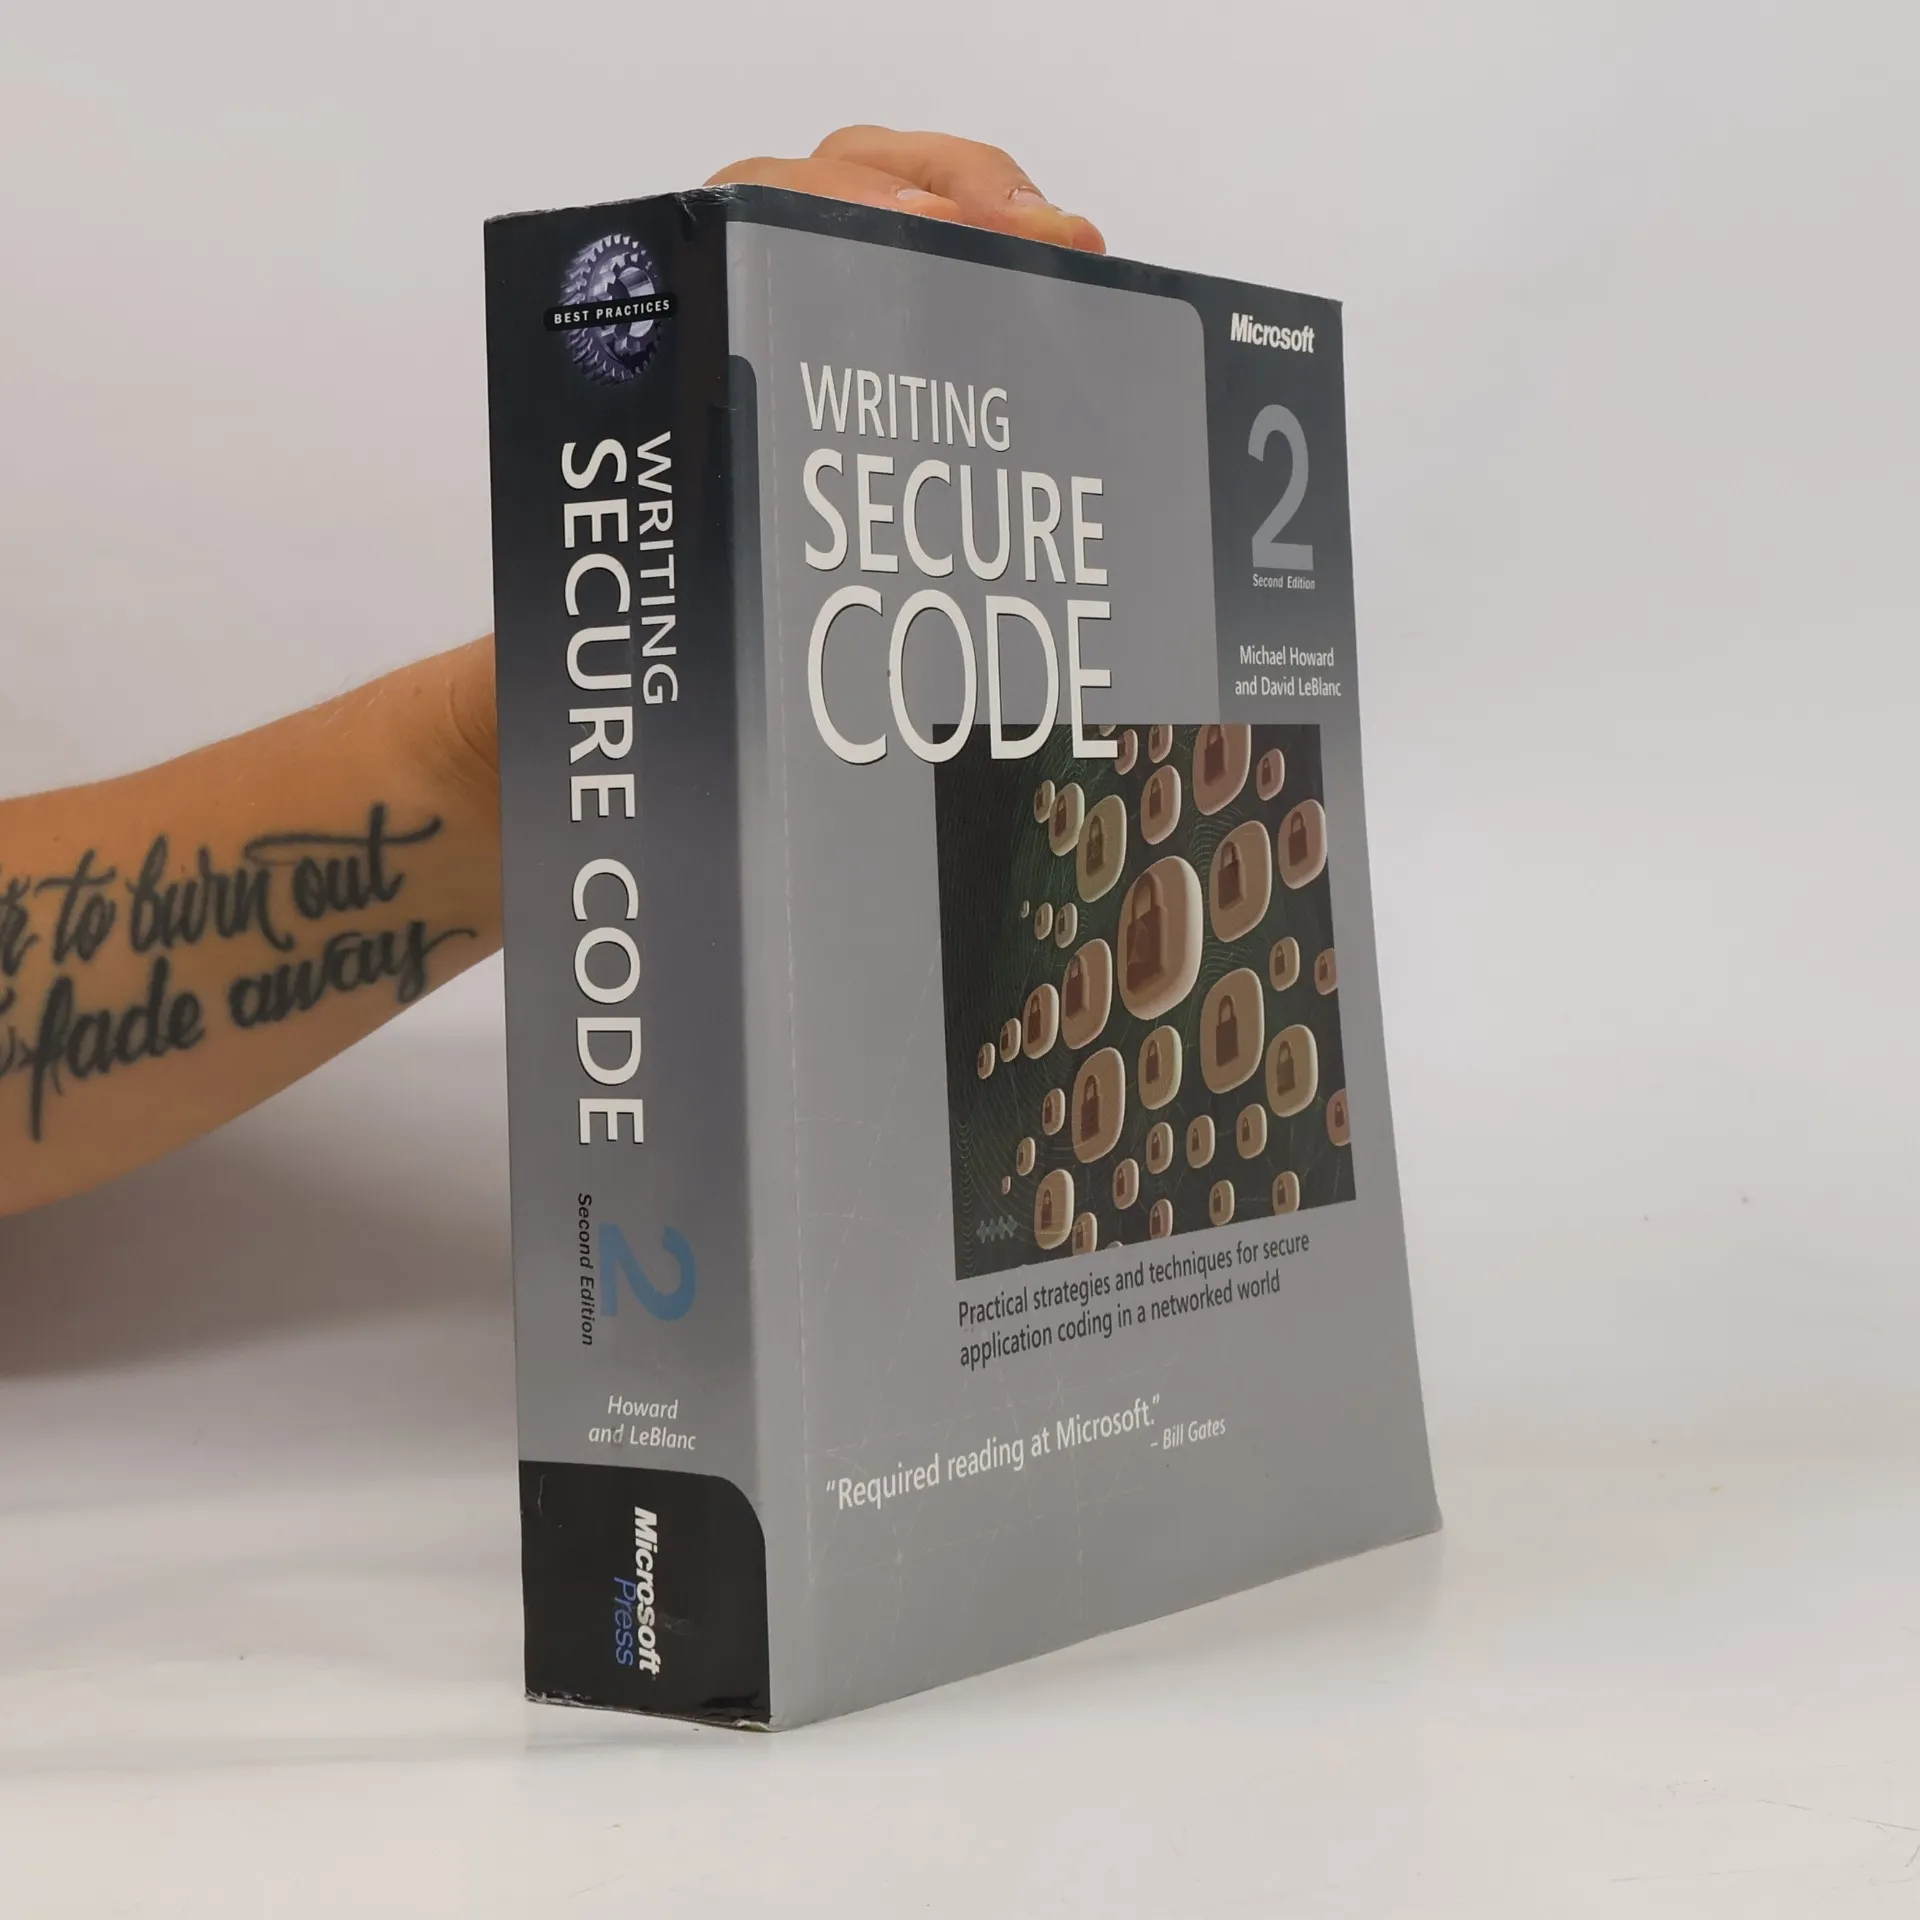
Writing Secure Code
Practical Strategies and Techniques for Secure Application Coding in a Networked World - Second Edition
Authors
Book rating
More about the book
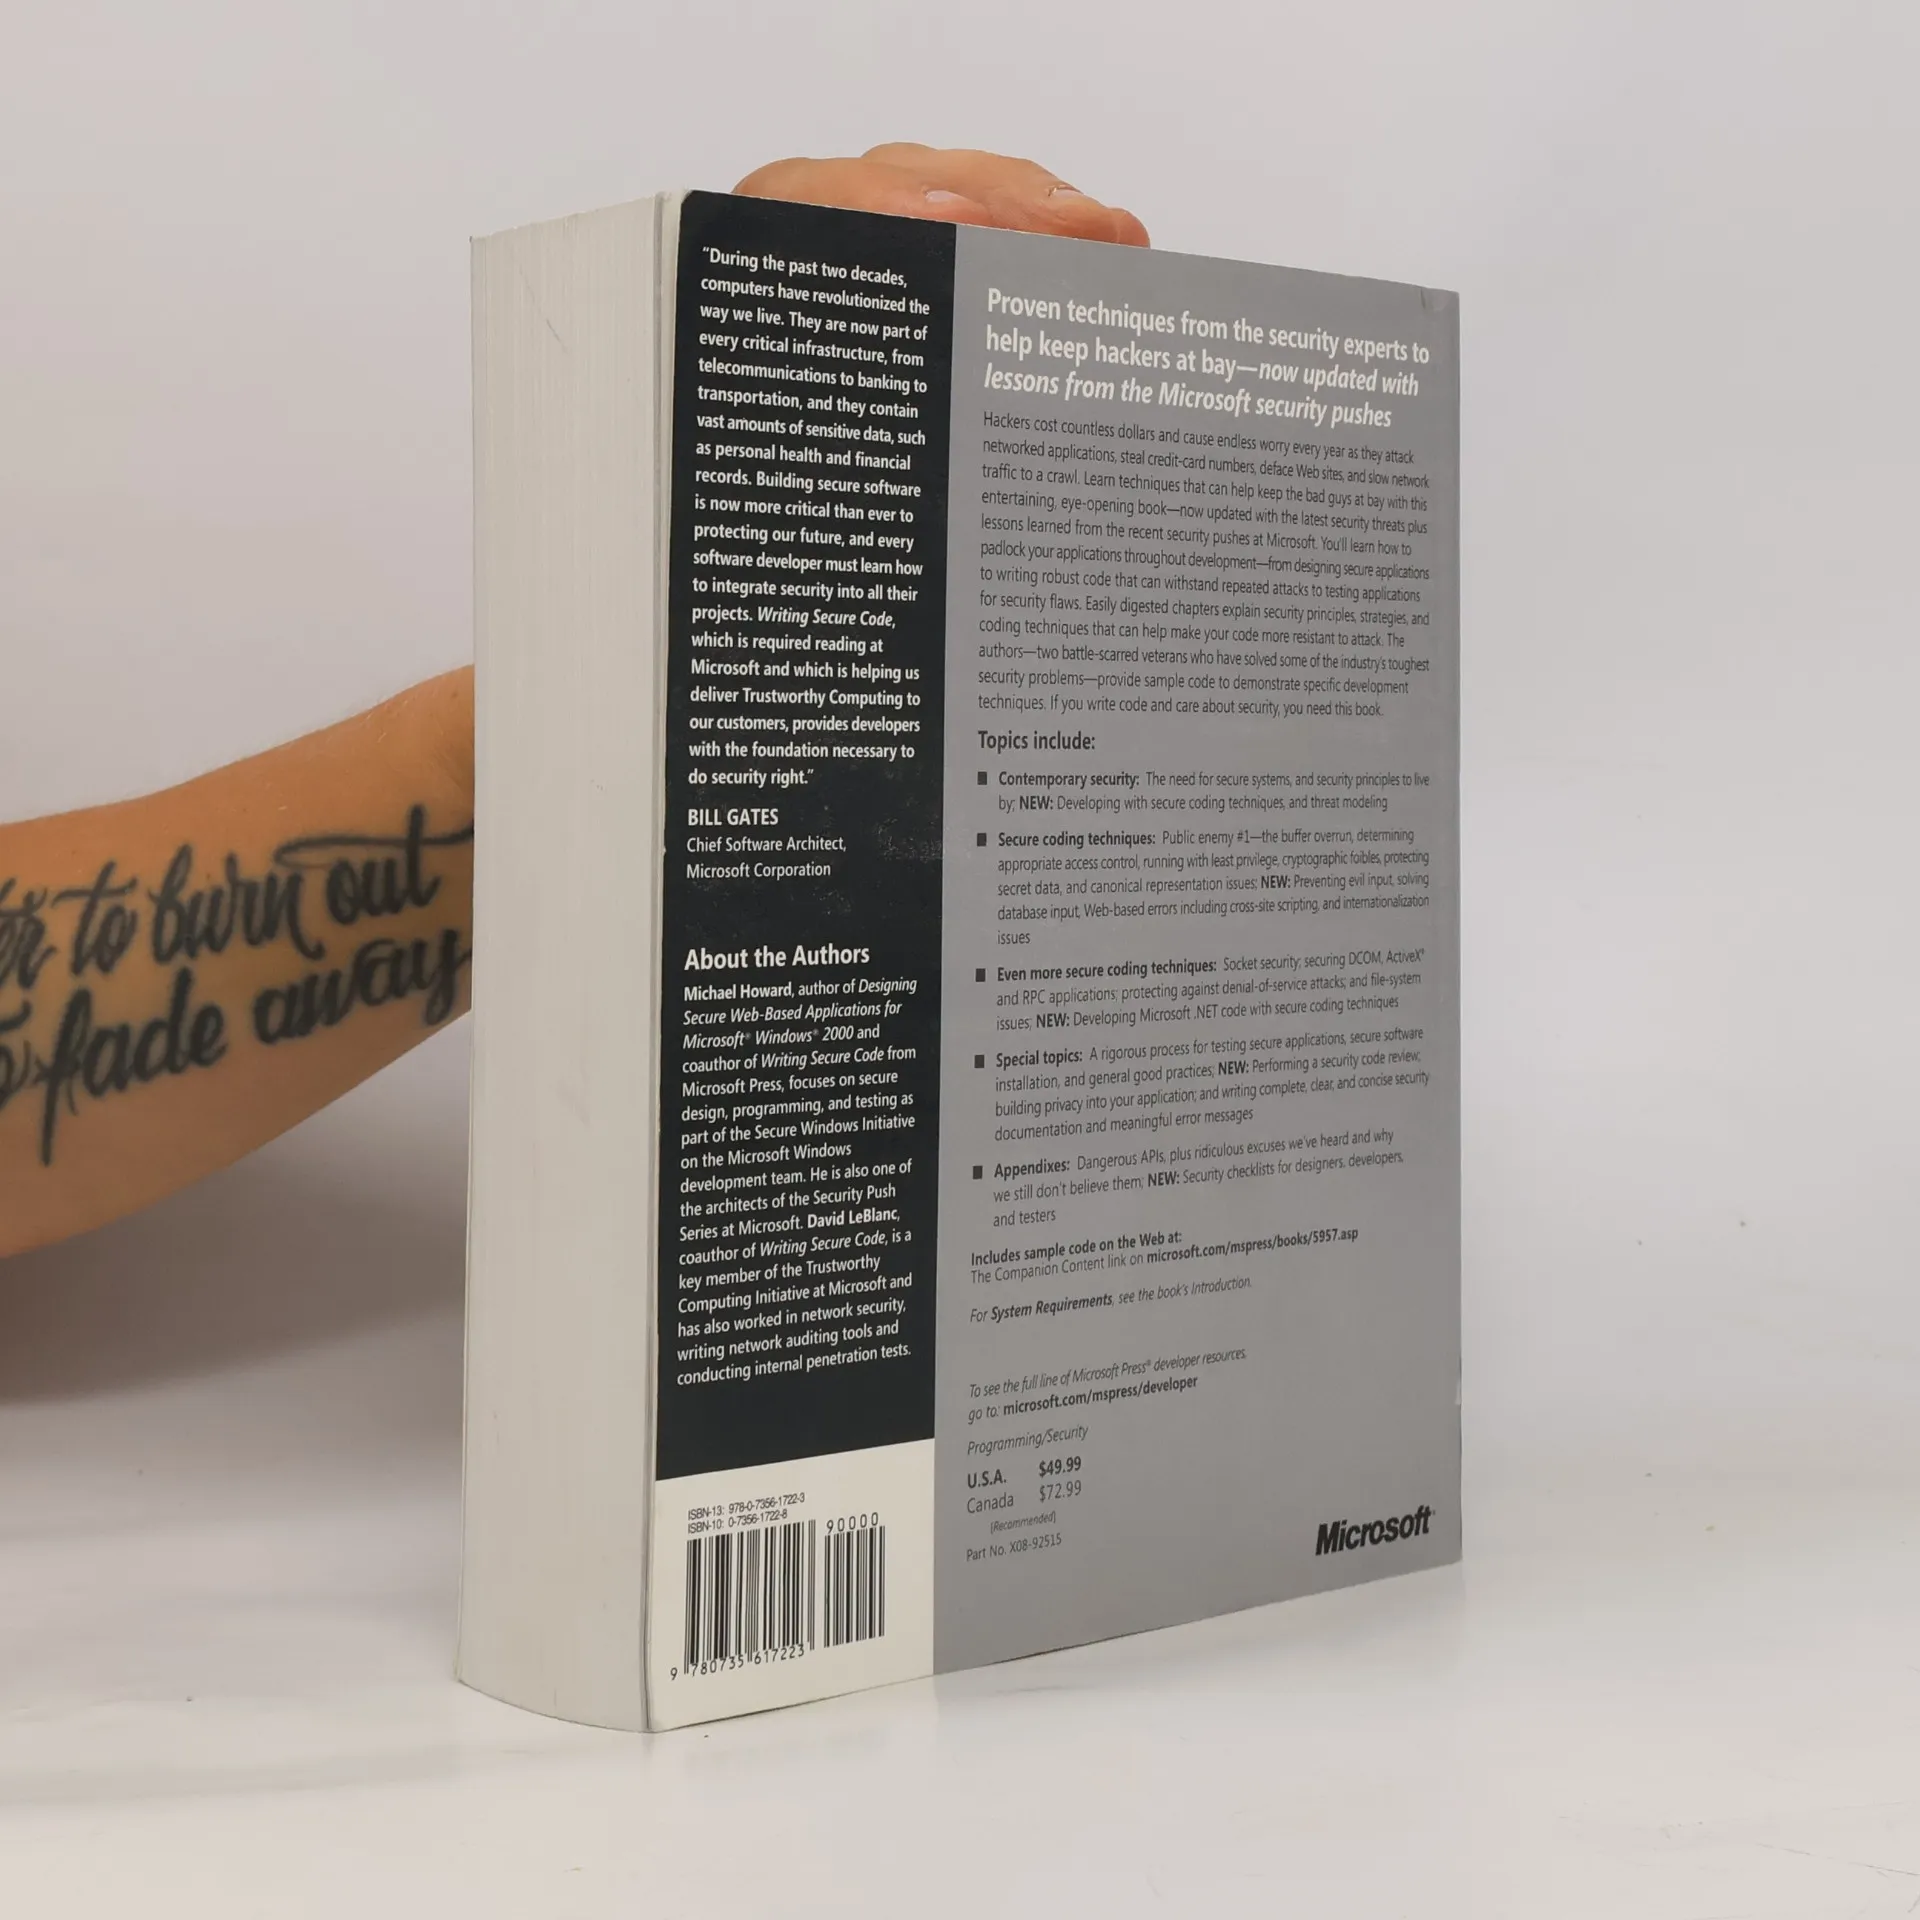
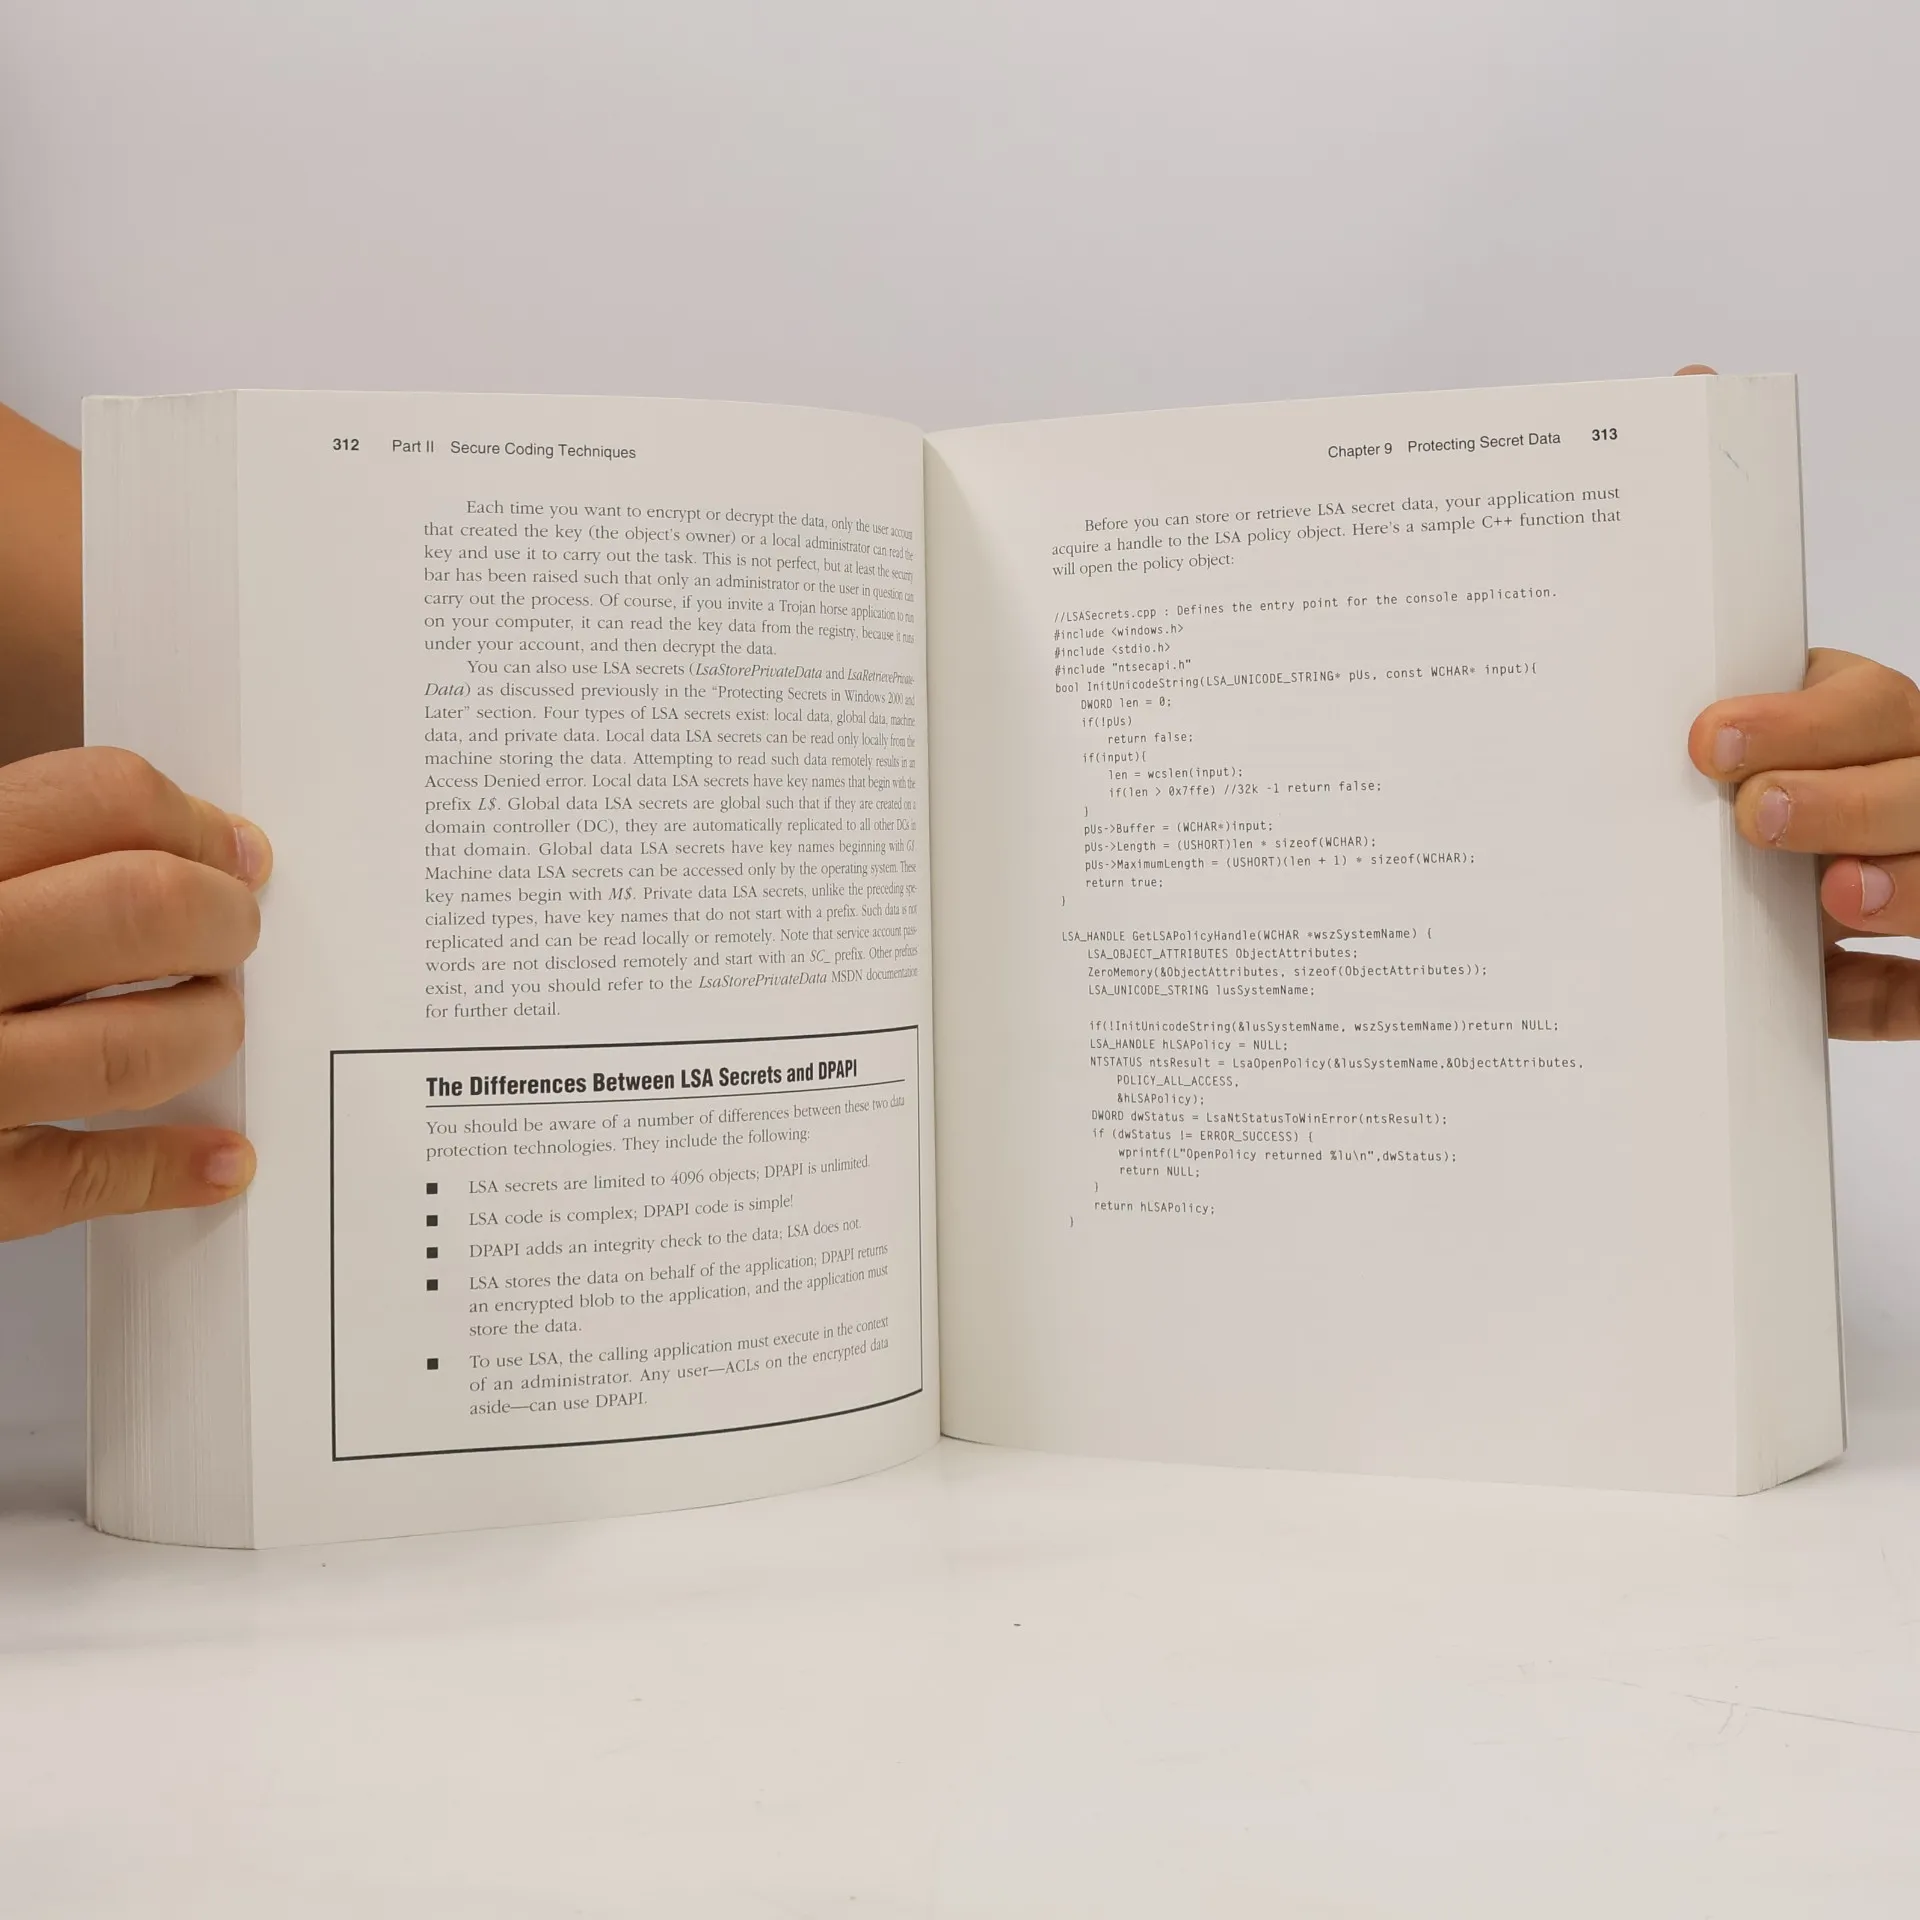
Your code will be attacked. You need to design, code, and test with the assumption that it will run in hostile environments. This book shows you how, drawing on lessons from Microsoft's 2002 Windows Security Push. It significantly upgrades the First Edition with new insights. The authors help you define security for your customers and implement a strategy focusing on design, defaults, and deployment. A key feature is threat modeling, which involves breaking down your application, identifying threats, ranking them, and mitigating them. The book delves into critical security issues from a developer's perspective, including a full chapter on avoiding buffer overruns. You'll learn to establish proper access controls and adopt a least privilege approach. There’s also detailed guidance on countering cryptography attacks, such as avoiding poor random numbers and bit-flipping. The book offers countermeasures for various user input attacks, including malicious database updates and cross-site scripting. Techniques for securing sockets, protecting against DOS attacks, building safer .NET applications, and writing high-quality security documentation are also covered. Following these techniques will enhance security and significantly improve robustness and reliability.
Language


Book purchase
Writing Secure Code, Michael Howard, David LeBlanc
- Language

- Released
- 2005
- Binding
- (Paperback)
Payment methods
We’re missing your review here.
- Title
- Writing Secure Code
- Subtitle
- Practical Strategies and Techniques for Secure Application Coding in a Networked World - Second Edition
- Language
- English
- Authors
- Michael Howard, David LeBlanc
- Publisher
- Microsoft Press
- Released
- 2005
- Format
- Paperback
- Pages
- 768
- ISBN10
- 0735617228
- ISBN13
- 9780735617223
- Series
- Tags
- References & Manuals, Technology, Software, Web Development, Software Development, Internet Security
- Original title
- Writing Secure Code & Writing Secure Code for Windows Vista
- Rating
- 3.25 out of 5
- Description
- Your code will be attacked. You need to design, code, and test with the assumption that it will run in hostile environments. This book shows you how, drawing on lessons from Microsoft's 2002 Windows Security Push. It significantly upgrades the First Edition with new insights. The authors help you define security for your customers and implement a strategy focusing on design, defaults, and deployment. A key feature is threat modeling, which involves breaking down your application, identifying threats, ranking them, and mitigating them. The book delves into critical security issues from a developer's perspective, including a full chapter on avoiding buffer overruns. You'll learn to establish proper access controls and adopt a least privilege approach. There’s also detailed guidance on countering cryptography attacks, such as avoiding poor random numbers and bit-flipping. The book offers countermeasures for various user input attacks, including malicious database updates and cross-site scripting. Techniques for securing sockets, protecting against DOS attacks, building safer .NET applications, and writing high-quality security documentation are also covered. Following these techniques will enhance security and significantly improve robustness and reliability.